NEW
Enactia for MSPs — the vCISO & vDPO platform
  • Contact Us
  • Request Demo
Linkedin-in X-twitter Youtube Facebook-f Instagram
Enactia GRC logo
  • Platform

    Compliance

    • Compliance Assessments
    • Compliance Universe
    • Policy Management
    • Document Repository & Evidence

    Privacy

    • Record of Processing (ROPA)
    • DPIAs
    • Data Subject / Consumer Requests
    • Incident & Data Breach

    Risk & operations

    • Enterprise Risk Management
    • Vendor & Third Party
    • Asset Management
    • Ticketing & Task Management
    • Whistleblowing Management
    ISO 27001SOC 2GDPRControlsRisksVendorsAI

    AI cross-mapping

    One AI-powered GRC platform that cross-maps your controls, risks and vendors.

    See Compliance Universe →

    Ready to simplify compliance?
    See how one AI-powered GRC platform brings compliance, privacy and risk together.
    Start a Free Trial
  • Solutions

    By role

    • CISO
    • DPO
    • IT Governance Officer
    • Risk Management Officer
    • vCISO
    • vDPO

    By regulation

    • GDPR (EU)
    • DORA (EU)
    • HIPAA (US)
    • CCPA (California)
    • KSA PDPL (Saudi Arabia)
    • DIFC Data Protection Law (UAE)

    All regulations →

    By framework

    • ISO 27001
    • ISO 42001
    • SOC 2 (AICPA)
    • NIST Cybersecurity
    • PCI-DSS
    • Cloud Control Matrix (CCM)

    All frameworks →

    Client AClient BClient CMSP
    New

    Enactia for MSPs

    The vCISO & vDPO platform for managed service providers running compliance for many clients.

    Explore MSP edition →

    Not sure where to start?
    Tell us about your role and the regulations you work with.
    Talk to us
  • Services

    Professional services

    • Onboarding & Migration
    • Training
    • Tailored Solution
    • Customised Templates
    • On-Premise Installation

    Get started

    • Request a demo
    • Licensing & pricing
    • Contact us
    Partners
    Become our Partner
    Add white-label GRC and NIS2 services to what you offer your clients.
    • White-label GRC
    • NIS2 services for MSPs
    Explore partnership
    MSPvCISOvDPOWhite-labelEnactia
    Talk to our team
    Plan onboarding, migration or a tailored rollout.
    Contact us
  • Resources
    Learn
    Compliance Guides
    Practical guides to frameworks and regulations.
    Learn
    White Papers & Publications
    In-depth reading on GRC topics.
    Learn
    Enactia Blog
    Insights and updates from the Enactia team.
    Free tools
    All Free Tools
    Browse our free compliance tools.
    Engage
    Webinars
    Watch sessions on compliance and risk.
    Engage
    Events & Conferences
    See where to meet the Enactia team.
    Engage
    Certification Program
    Learn about Enactia's certification program.
    Free tool
    NIS2 scope checker
    Find out whether NIS2 applies to your organisation.
  • Company
    About
    Meet Enactia
    The company, team and customers behind the platform.
    Meet our Company →
    Meet our team
    Our Customers
    Our Awards
    Careers
    Become our Partner
    Contact us
    From the blog
    Enactia unveils Compliance Universe and Policy Management.
    Read more →
  • Licensing
Request trial
  • Michael Pittas
  • January 25, 2026January 26, 2026

The Compliance Triple Threat: Mastering the Overlap Between DORA, NIS2, and the EU AI Act

In 2026, the European regulatory landscape has reached a "tipping point." CISOs and DPOs ...

Read More
  • Michael Pittas
  • January 21, 2026January 26, 2026

Mastering DORA Compliance in 2026

With the Digital Operational Resilience Act (DORA) now fully enforceable, the financial sector has ...
Read More
Enactia Unveils “Compliance Universe” and “Policy Management” – A New Era of GRC Excellence
AIEnactiaGRC
  • Michael Pittas
  • January 18, 2026October 22, 2026

Enactia Unveils “Compliance Universe” and “Policy Management” – A New Era of GRC Excellence

In today’s hyper-regulated environment, senior risk and compliance professionals face mounting pressure to stay ...

Read More
Introducing EnactAI Compliance Assistant!
AIGRC
  • Michael Pittas
  • October 15, 2024October 22, 2026

Introducing EnactAI Compliance Assistant!

We are thrilled to announce that in our upcoming software update, we will be ...
Read More
Read Our Co-Founder Christos Makedonas’ Exclusive Interview with SafetyDetectives!
CyberData ProtectionGCCGRC
  • Michael Pittas
  • August 30, 2024October 22, 2026

Read Our Co-Founder Christos Makedonas’ Exclusive Interview with SafetyDetectives!

We're excited to share that our Co-Founder, Christos Makedonas, recently sat down with Shauli ...

Read More
The CrowdStrike Incident: A Wake-Up Call for Enhanced Cybersecurity Governance and Quality Assurance
CyberEuropean Union
  • Michael Pittas
  • July 31, 2024October 22, 2026

The CrowdStrike Incident: A Wake-Up Call for Enhanced Cybersecurity Governance and Quality Assurance

In today's digital age, cybersecurity has become a critical concern for businesses worldwide. The ...

Read More
European Parliament Passes Groundbreaking Legislation on Artificial Intelligence
AIEuropean Union
  • Michael Pittas
  • March 13, 2024October 22, 2026

European Parliament Passes Groundbreaking Legislation on Artificial Intelligence

Today, 13th of March 2024, the European Parliament has approved the Artificial Intelligence Act. ...
Read More
Introducing NIST Cybersecurity Framework 2.0: Expanded and Enhanced for All Organization
Cyber
  • Michael Pittas
  • February 26, 2024October 22, 2026

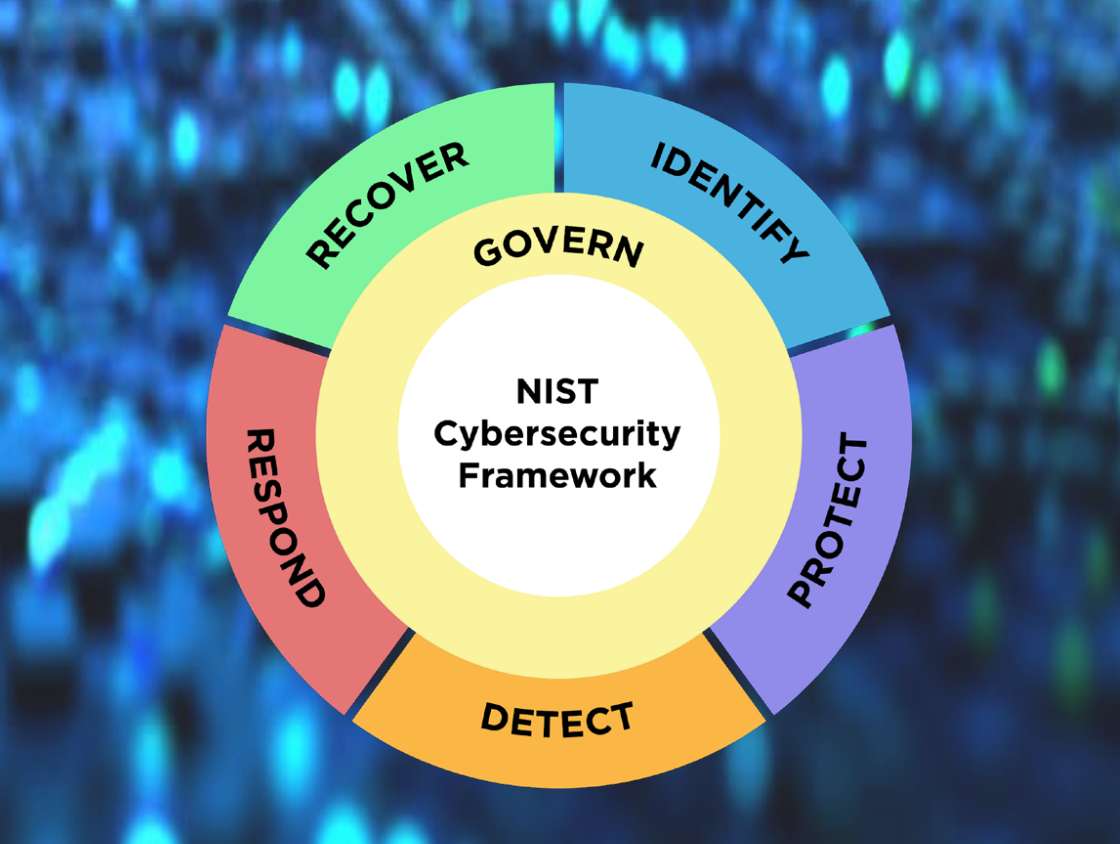
Introducing NIST Cybersecurity Framework 2.0: Expanded and Enhanced for All Organization

The National Institute of Standards and Technology (NIST) has released an updated version of ...

Read More
EU adobts the first EU-wide cybersecurity certification scheme, as outlined in the EU Cybersecurity Act
CyberEuropean Union
  • Michael Pittas
  • February 1, 2024October 22, 2026

EU adobts the first EU-wide cybersecurity certification scheme, as outlined in the EU Cybersecurity Act

The European Commission has launched the first EU-wide cybersecurity certification scheme, as outlined in ...

Read More
IAPP released Global Legislative Predictions 2024 and our Co-Founder shares his views
Data Protection
  • Michael Pittas
  • January 24, 2024October 22, 2026

IAPP released Global Legislative Predictions 2024 and our Co-Founder shares his views

Our Co-founder, Christos Makedonas has contributed to this insightful publication and represented also hashtag#Cyprus. ...
Read More

Recent Posts

  • NIST SP 800-53: A Practical Overview for CISOsNovember 11, 2026
  • GDPR Compliance Services for MSPs: How to Build ThemNovember 11, 2026
  • EU AI Act GPAI Obligations: A Practical Compliance GuideNovember 10, 2026

Categories

  • Agency
  • AI
  • CSR
  • Cyber
  • Data Protection
  • Design
  • Development
  • Enactia
  • European Union
  • Events & Conferences
  • GCC
  • GRC
  • Partnerships
  • Software
  • USA
  • Webinars
  • White Papers & Publications

Tags

AI AI Governance Certification CISO Compliance Automation Cyber Governance Cybersecurity Data Privacy Data Protection DIFC DORA DPO DSAR enactia EU EU AI Act Financial services GCC GDPR GRC GRC Platform GRC software HIPAA ICT risk management Incident Reporting Internal Audit ISMS ISO 27001 ISO 42001 KSA MSP MSSP NIS2 NIS2 compliance NIST NIST CSF Operational Resilience Risk Assessment Risk Management Supply Chain Security Third-Party Risk Management UAE UK GDPR vCISO vDPO

  • 1
  • …
  • 11
  • 12
  • 13
  • 14
  • 15

Governance, Risk & Compliance made simple

Up to 80% less compliance effort across 50+ frameworks.

One GRC platform for cybersecurity, data protection and AI governance — with AI cross-mapping, so evidence collected once counts everywhere.

Request a demo
Start a free trial
  • Free · 2-minute check

Is your organisation in scope for NIS2?

Find out whether NIS2 applies to you — and whether you’re an essential or important entity.

Run the NIS2 Scope Checker
  • NIS2 transposition tracker by EU country
  • GRC guides: NIS2, DORA, ISO 27001, GDPR
  • All free compliance tools
Enactia GRC logo

Enactia is a governance, risk and compliance (GRC) platform for cybersecurity, data protection and AI governance. Automate ISO 27001, SOC 2, NIS2, DORA, GDPR and 50+ frameworks and laws from one workspace.

Linkedin-in X-twitter Youtube Facebook-f Instagram
  • ISO/IEC 27001 certified
  • SOC 2 compliant

Security statement →

Platform

  • Platform overview
  • Compliance assessments
  • Compliance universe
  • Policy management
  • Enterprise risk management
  • Vendor & third-party risk
  • ROPA
  • DPIAs
  • DSAR & consumer requests
  • Incident & breach management
  • Asset management
  • Evidence management
  • Ticketing & tasks
  • Whistleblowing

Frameworks

  • ISO 27001
  • ISO 27701
  • ISO 42001
  • ISO 22301
  • ISO 27005
  • SOC 2
  • NIST CSF 2.0
  • NIST SP 800-53
  • NIST Privacy Framework
  • PCI DSS
  • CIS Controls
  • Cloud Controls Matrix
  • Secure Controls Framework
  • KSA ECC
  • SAMA
  • All frameworks →

Regulations

  • GDPR
  • NIS2
  • DORA
  • EU AI Act
  • EU Cyber Resilience Act
  • CCPA
  • CPRA
  • HIPAA
  • KSA PDPL
  • UAE PDPL
  • DIFC Data Protection Law
  • ADGM DPR
  • Bahrain PDPL
  • India DPDP
  • Singapore PDPA
  • POPIA
  • All regulations →

Solutions

  • For CISOs
  • For DPOs
  • For IT governance
  • For risk managers
  • Enactia for MSPs
  • vCISO platform
  • vDPO as a service
  • Multi-tenant GRC
  • White-label GRC
  • NIS2 services for MSPs
  • Professional services
  • On-premise deployment

Resources

  • GRC guides
  • Enactia blog
  • What is GRC?
  • Free compliance tools
  • NIS2 scope checker
  • NIS2 transposition tracker
  • Webinars
  • Events & conferences
  • White papers
  • Certification program
  • Knowledge base

Company

  • About Enactia
  • Meet our company
  • Meet our team
  • Customers
  • Awards
  • Careers
  • Become a partner
  • Licensing & pricing
  • Request a demo
  • Contact us

© 2026 Enactia Ltd. All rights reserved

  • Privacy Policy
  • Cookie Policy
  • Terms & Conditions
  • Disclaimer
  • Refund Policy
  • Information Security Statement
Cookie settings
Enactia - Governance, Risk & Compliance made Simple
Enactia Cookie Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}