
The vCISO & vDPO platform built for MSPs.
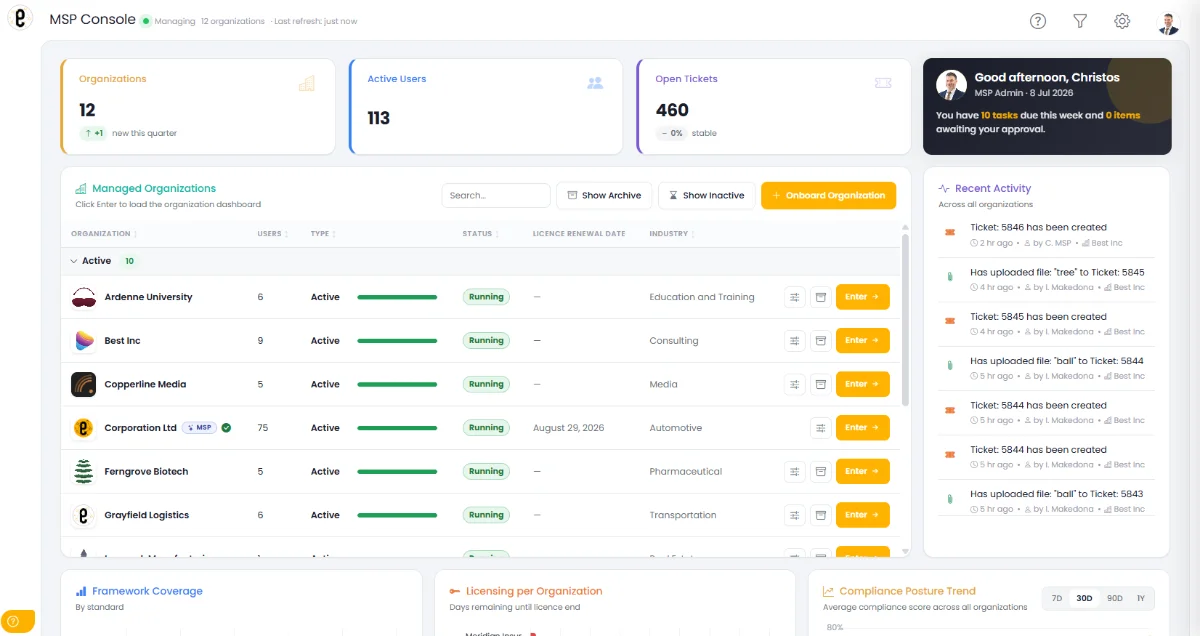
The multi-tenant GRC platform that lets service providers deliver virtual CISO and virtual DPO services to every client they manage – privacy and security, one intelligent workspace, clean margins.
Growing a practice shouldn't mean growing the chaos.
Most GRC tools were built for a single company, then bent to fit a practice. Run a book of clients on them and the day disappears into hunting for evidence and switching logins.
Sprawl, times every client
Each org has its own spreadsheets, drives and evidence folders. Multiply that by twenty clients and the day disappears into hunting.
Tools that assume one company
Most GRC software was built for a single organisation, then bent to fit a practice. Switching tenants means switching logins.
Privacy and security, split apart
A DPO tool here, a security tool there. The same client answered twice, in two systems that never talk.
Margins eaten by manual work
Advisory time billed at a premium, spent instead copying findings into reports and chasing evidence by email.
Hard to prove the value
Clients ask “are we compliant?” and the answer is a slide pack assembled by hand the night before the QBR.
Onboarding takes weeks
Every new client is a fresh setup from scratch – no templates, no inheritance, no head start.
Run vDPO and vCISO from the same graph.
Privacy and security stop living in separate silos. A client answers once, and the work informs both disciplines – for every organisation in your book.
Data Protection compliance, automated & managed.
Deliver a complete virtual Data Protection Officer service for every client – the privacy programme runs itself, you run the relationship.
ROPA management
Auto-generate Records of Processing Activities per client org, audit-ready.
DPIA workflow
Guided impact assessments with risk scoring and multi-level approval routing.
Breach notification
72-hour workflows with supervisory-authority templates and full evidence capture.
DSR management
End-to-end data subject requests – intake, verification, fulfilment and audit trail.
AI on data & regulation
Guidance on data-protection articles, national implementations and obligations.
DPA designation letters
Auto-generate authority designation and mission letters for each client org.
Security leadership, delivered as a service.
A virtual Chief Information Security Officer for every client – covering NIS2, ISO 27001, DORA, the EU AI Act, NIST CSF and much more, from one console.
Risk register
Identification, scoring and treatment plans aligned to ISO 27001, NIS2 and more.
Policy management
Customisable templates – acceptable use, incident response, BCP, privacy – per org.
Compliance assessments
Benchmark each client against industry frameworks and track improvement over time.
Incident management
The full lifecycle – detect, contain, eradicate, recover and report – with audit trail.
Asset & vendor management
Central asset inventories and third-party risk assessments across all client orgs.
AI security guidance
Guidance on NIS2, DORA and ISO 27001 obligations, with control recommendations.
Every module. You decide who gets what.
The full Enactia platform is included in your MSP licence – nothing gated, nothing extra. Hover to explore, tap any tile for the detail. Switch modules on per client, so the service fits the org in front of you.
Compliance Universe
AI cross-maps your controls across every framework in scope – comply once, apply everywhere.
Compliance Assessments
Measure posture against every applicable law, framework and standard.
Policy Management
Author, approve, publish and track acknowledgement of every policy.
Enterprise Risk Management
Identify, score, mitigate and monitor risk across the organisation.
DPIAs
Structured impact assessments with linked risks and safeguards.
ROPA
The living Record of Processing Activities – wired into every other module in the graph.
Vendor & Third Party
Onboard, assess, score and monitor every external relationship.
Incident & Breach
Register, triage, notify and document to every regulator that needs it.
Data Subject Requests
Never miss a DSR deadline. Workflows for every regulation.
Asset Management
Map data, systems and processes, and the risks attached to them.
AI Governance & Assistant
A generative layer woven through every module – it drafts the work, you keep the judgement.
Actions & Tasks
One inbox for compliance work. Every task tied to a control.
Document Repository
Versioned evidence, signed off and audit-ready.
Whistleblowing
EU-Directive-aligned anonymous and secure reporting channel.
Steering Committee
Govern compliance forums end-to-end.
Vulnerability & Penetration Testing
Scanner results, pentest projects and asset-linked vulnerability management.
Complaints Management
Centralise customer, employee and regulator complaints.
all included
One platform for every client's regulatory map.
Pay for exactly what you run.
One flat rate per organisation – every service and module included, no per-user fees, no surprises. Billing flexes with your book.
Pay for ten, get twelve.
Commit for the year and roughly two months are free, across every active organisation – your best margin.
Per org, month to month.
A flat fee per active client organisation, billed monthly. Add an org the moment you win a client.
Done with a client? Archive it.
Stop managing a client? Archive the org and billing stops at once – you only pay for active orgs.
vDPO + vCISO and every module included in the flat rate – no upsells.
Your logo, colours and domain on every portal and report – no extra fee.
Every consultant and client user, every assessment and evidence file – no caps.
Practices that run on Enactia.
Find a provider to run it for you.
Looking for a consulting firm or independent expert to deliver your virtual DPO, virtual CISO – or both – as a managed service? These certified partners run it on Enactia, so you get seasoned advisory judgement backed by the intelligence of the platform. Browse them below and reach out directly.
You need the service
A managed vDPO, vCISO or both – without hiring in-house.
A partner delivers it
A certified firm or expert brings the advisory judgement and sector context.
Powered by Enactia
The platform automates the evidence, mapping and reporting underneath.
Grant Thornton
Grant Thornton’s Digital Risk practice delivers vCISO and vDPO-as-a-Service, giving organisations on-demand executive security and data-protection leadership backed by a full GRC and compliance team. It pairs regulatory depth across GDPR, NIS2, DORA and ISO 27001 with the assurance and independence of an established professional-services firm.
CyberFlip
Cybersecurity firm offering CISO-as-a-Service (vCISO) and vDPO built around its “flipped” Zero Trust framework, which reverses the security lifecycle from recovery to protection. It provides vendor-neutral, quantitative cyber risk management, supply-chain threat analysis and cyber-maturity services tailored to each client’s needs and budget.
Uni Systems
A long-established Greek IT systems integrator (Quest Group) whose Cybersecurity & Compliance practice covers Governance, Risk & Compliance, security consulting and 24/7 incident response. It takes a holistic approach to protecting information assets and ensuring compliance, complemented by offensive and assurance testing.
Become an Enactia partner.
Join the network, get certified, and run a profitable vCISO & vDPO practice on the platform built for it – with your firm featured here in front of prospective clients.
Everything an MSP asks first.
Is the platform really multi-tenant?
Yes – built for it from the ground up, not retrofitted. Every client organisation lives in its own isolated, secure tenant, and you manage them all from a single MSP console. Switch context in a click; the data never mixes.
Does Enactia ever sell directly to my clients?
Never. Enactia is partner-first by design. Your client relationship and your revenue stay yours – we power the practice, we don’t compete with it. Clients receive a portal branded entirely as you, with no direct Enactia deal.
What's included in the licence?
Everything. All 16 modules, both vDPO and vCISO services, unlimited internal and client users, white-label portals and reports, and two demo organisations with rolling 15-day trials – all in one flat rate per active organisation. Nothing is gated behind add-ons.
How does the pricing work as I scale?
A single flat fee per active client organisation – monthly or annually (annual is roughly two months free). Add an org when you win a client, archive it when you part ways and billing stops immediately. No per-user fees, so your margin is trivial to calculate.
Which frameworks and laws are covered?
50+ frameworks and standards (ISO 27001, NIS2, DORA, SOC 2, the EU AI Act, NIST CSF and more) plus data-protection laws across Europe, the Americas, the Middle East, Africa and APAC. Map a control once and it inherits across every framework a client touches – and we add new ones on request at no extra cost.
Can I white-label the client experience?
Yes, as standard. Apply your logo, colours and domain to every client portal and to the auto-generated reports and board packs your clients receive. The service looks like yours, because it is.
How is it deployed?
Enactia is a fully managed cloud SaaS platform, hosted and maintained by us so there is nothing to run or patch yourself. Our team supports migration and data import from your current tools as part of onboarding.
Start a running practice in four steps.
Book a guided partner demo – run against your own frameworks and a sample client book – and see the multi-tenant platform, white-label portal and margin model end to end.
The multi-tenant GRC platform purpose-built for MSPs running virtual DPO and virtual CISO practices.
