

• Contact Us
  • Request Demo
Linkedin X-twitter Youtube Facebook Instagram
Enactia GRC logo
Request Trial
  • About‎‎‎

    Meet our Company

    Our Story and Mission

    Meet our team

    Discover Our Dynamic Team

    Our Awards

    Proud of our Achievements

    Our Customers

    Building strong Relationships

    Enactia Blog

    Latest News & Our Views

    Careers

    Working with Talented Individuals

  • Our Solution

    By Role

    • Chief Information Security Officer (CISO)
    • Data Protection Officer (DPO)
    • IT Governance Officer
    • Risk Management Officer
    • Virtual CISO (vCISO)
    • Virtual DPO (vDPO)
    Compliance Universe and Policy Management GRC tool

    Enactia Unveils “Compliance Universe” and “Policy Management” – A New Era of GRC Excellence

    January 18, 2026
    Read More »

    By Regulation

    • GDPR (EU)
    • CCPA (California)
    • DORA (EU)
    • DIFC Data Protection Law (UAE)
    • ADGM DPR (UAE)
    • KSA PDPL (Saudi Arabia)
    • PDPL (Bahrain)
    • PIPEDA (Canada)
    • POPIA (South Africa)
    • PDPA (Singapore)
    • HIPAA (US)
    • Explore More

    By Framework

    • ISO 27001
    • ISO 27701
    • ISO 42001
    • NIST Cybersecurity
    • Cloud Control Matrix (CCM)
    • NIST Privacy
    • SOC 2 (AICPA)
    • PCI-DSS
    • EBA PSD2
    • EBA ICT & Security Risk Management
    • Saudi Arabian Monetary Authority
    • Explore More
  • Platform

    Enactia Modules

    • Compliance Assessments
    • Policy Management
    • Compliance Universe
    • Record of Processing Activities (ROPA)
    • Enterprise Risk Management
    • Data Protection Impact Assessments (DPIAs)
    • Vendor & Third Party Management
    • Incident & Data Breach Management
    • Data Subject / Consumer Requests
    • Asset Management
    • Ticketing & Task Management
    • Document Repository & Evidence Management
    • Whistleblowing Management
  • Services

    Become our Partner

    Enactia governance, risk, and compliance software dashboard showing centralized controls and compliance modules

    Professional Services

    • Onboarding & Migration
    • Training
    • Tailored Solution
    • Customised Templates
    • On-Premise Installation
  • Resources

    Compliance Guides

    GDPR, NIS2, DORA & more

    Events & Conferences

    Bringing our Ideas to Life

    Webinars

    Connect, Learn, Grow Together

    White Papers & Publications

    Unlocking Indutry Insights

    Certification Program

    Elevate Your Expertise Now

    Knowledge Base

    Guidance and Training

  • Licensing
Enactia company logo symbolizing governance, risk, and compliance management
Request Trial
  • About‎‎‎

    Meet our Company

    Our Story and Mission

    Meet our team

    Discover Our Dynamic Team

    Our Awards

    Proud of our Achievements

    Our Customers

    Building strong Relationships

    Enactia Blog

    Latest News & Our Views

    Careers

    Working with Talented Individuals

  • Our Solution

    By Role

    • Chief Information Security Officer (CISO)
    • Data Protection Officer (DPO)
    • IT Governance Officer
    • Risk Management Officer
    • Virtual CISO (vCISO)
    • Virtual DPO (vDPO)
    Compliance Universe and Policy Management GRC tool

    Enactia Unveils “Compliance Universe” and “Policy Management” – A New Era of GRC Excellence

    January 18, 2026
    Read More »

    By Regulation

    • GDPR
    • CCPA (California)
    • DIFC Data Protection Law (UAE)
    • ADGM DPR (UAE)
    • KSA PDPL (Saudi Arabia)
    • Bahrain PDPL
    • PIPEDA (Canada)
    • POPIA (South Africa)
    • Singapore PDPA
    • HIPAA (US)
    • DORA (EU)
    • Explore More

    By Framework

    • ISO 27001
    • ISO 27701
    • ISO 42001
    • NIST Cybersecurity
    • Cloud Control Matrix (CCM)
    • NIST Privacy
    • SOC 2 (AICPA)
    • PCI-DSS
    • EBA PSD2
    • EBA ICT & Security Risk Management
    • Saudi Arabian Monetary Authority
    • Explore More
  • Platform

    Enactia Modules

    • Compliance Assessments
    • Policy Management
    • Compliance Universe
    • Record of Processing Activities (ROPA)
    • Enterprise Risk Management
    • Data Protection Impact Assessments (DPIAs)
    • Vendor & Third Party Management
    • Incident & Data Breach Management
    • Data Subject / Consumer Requests
    • Asset Management
    • Ticketing & Task Management
    • Document Repository & Evidence Management
    • Whistleblowing Management
  • Services

    Become our Partner

    Enactia governance, risk, and compliance software dashboard showing centralized controls and compliance modules

    Professional Services

    • Onboarding & Migration
    • Training
    • Tailored Solution
    • Customised Templates
    • On-Premise Installation
  • Resources

    Compliance Guides

    GDPR, NIS2, DORA & more

    Events & Conferences

    Bringing our Ideas to Life

    Webinars

    Connect, Learn, Grow Together

    White Papers & Publications

    Unlocking Indutry Insights

    Certification Program

    Elevate Your Expertise Now

    Knowledge Base

    Guidance and Training

  • Licensing
  • Michael Pittas
  • February 28, 2026March 10, 2026

DORA Compliance for UK Financial Services | Enactia

Although the Digital Operational Resilience Act (DORA) is an EU regulation, its impact on ...

Read More
  • Michael Pittas
  • February 27, 2026March 10, 2026

Online Safety Act (OSA) Compliance for UK Platforms | Enactia

By mid-2026, Ofcom’s enforcement of the Online Safety Act (OSA) has become a top ...

Read More
  • Michael Pittas
  • February 22, 2026March 10, 2026

Cyber Resilience & Risk Management for US Enterprises | Enactia

In 2026, the US market has shifted its focus from "Cybersecurity" (prevention) to "Cyber ...

Read More
  • Michael Pittas
  • February 21, 2026March 9, 2026

AI Governance & Compliance Guide for US CISOs 2026 | Enactia

As of March 2026, AI is no longer a "future project"—it is embedded in ...

Read More
  • Michael Pittas
  • February 18, 2026February 18, 2026

UK Business Compliance 2026: OSA, ECCTA, and Bribery Act Guide

1. The Online Safety Act (OSA) 2026With Ofcom now fully enforcing codes of practice, ...

Read More
  • Michael Pittas
  • February 6, 2026October 19, 2026

NCSC CAF 4.0 Guide 2026: Automating Cyber Assessment Framework Outcomes

Beyond the Checklist: Mastering the NCSC CAF 4.0 with Enactia In 2026, the NCSC Cyber ...
Read More
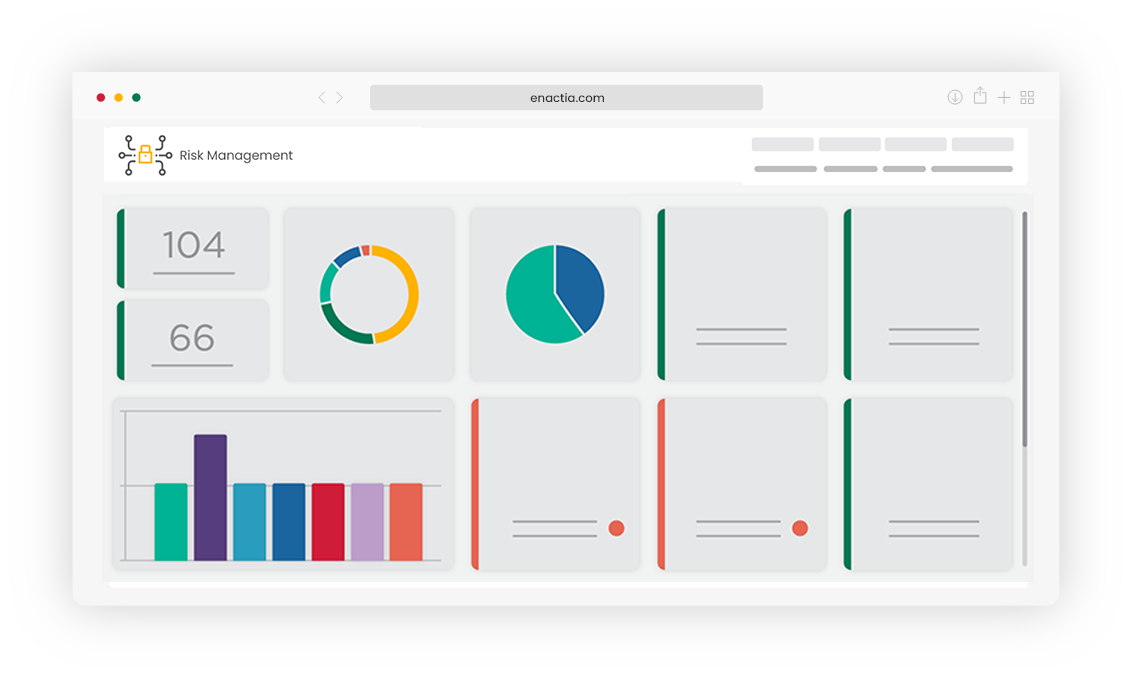
Risk Management Tools: Why Enactia is the Top GRC Choice
GRCSoftware
  • Michael Pittas
  • February 2, 2026February 2, 2026

Risk Management Tools: Why Enactia is the Top GRC Choice

In an era defined by rapid digital transformation and shifting regulatory landscapes, organizations can ...

Read More
  • Michael Pittas
  • January 28, 2026January 28, 2026

The Healthcare Modernizer (HIPAA)

The May 2026 HIPAA Security Rule overhaul has fundamentally changed the requirements for US ...

Read More
  • Michael Pittas
  • January 25, 2026January 26, 2026

The Compliance Triple Threat: Mastering the Overlap Between DORA, NIS2, and the EU AI Act

In 2026, the European regulatory landscape has reached a "tipping point." CISOs and DPOs ...

Read More
  • Michael Pittas
  • January 21, 2026January 26, 2026

Mastering DORA Compliance in 2026

With the Digital Operational Resilience Act (DORA) now fully enforceable, the financial sector has ...

Read More

Recent Posts

  • CMMC 2.0 Compliance Guide: Levels, Phases and 2026 StatusOctober 22, 2026
  • OneTrust Alternatives: How to Choose the Right Privacy and GRC PlatformOctober 22, 2026
  • US State Privacy Laws: A Compliance Guide for 2026October 22, 2026

Categories

  • Agency
  • AI
  • CSR
  • Cyber
  • Data Protection
  • Design
  • Development
  • Enactia
  • European Union
  • Events & Conferences
  • GCC
  • GRC
  • Partnerships
  • Software
  • USA
  • Webinars
  • White Papers & Publications

Tags

AI Certification CISO Compliance Automation Cyber Assessment Framework cyber resilience Cybersecurity Data Privacy Data Protection DIFC Digital Operational Resilience Act DORA DSAR enactia Enterprise Risk Management EU Financial services GCC GDPR GRC GRC Platform GRC software HIPAA ICT risk management Incident Reporting Internal Audit ISMS ISO 27001 KSA MSP MSSP NCSC CAF 4.0 NIS2 NIS2 compliance NIST NIST CSF Risk Assessment Risk Management Startup Supply Chain Security UAE UK CNI compliance UK GDPR vCISO vDPO

  • 1
  • …
  • 8
  • 9
  • 10
  • 11
  • 12
  • 13
Enactia GRC logo

Enactia serves as a comprehensive platform that addresses Governance, Risk, and Compliance (GRC) with a specific emphasis on compliance in the realms of Cybersecurity and Data Protection.

Linkedin X-twitter Facebook Youtube Instagram

About us

  • Meet our company
  • Our awards
  • Enactia blog
  • Careers
  • Contact us

Our Policies

  • Privacy Policy
  • Cookie Policy
  • Information Security Statement

Terms of Use

  • Terms & Conditions
  • Disclaimer
  • Refund Policy

Certified With

ISO 27001 certification logo representing information security management system standards.
SOC 2 certification logo representing compliance with data security and privacy standards.
Funded by D23 logo banner representing financial support or funding.

© 2026 Enactia Ltd – All rights reserved. 

Enactia - Governance, Risk & Compliance made Simple
Enactia Cookie Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}